

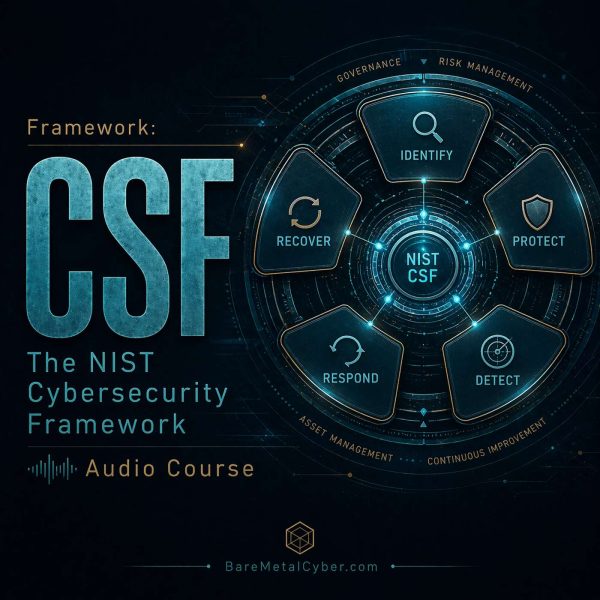
Framework: The NIST Cybersecurity Framework (CSF)
- Episódios
- 114
- Formato
- Série – ouça desde o começo
- Último episódio
- 14 out 2025
Sobre o podcast
**Framework** is your go-to podcast for mastering the **NIST Cybersecurity Framework (CSF)**—the foundational model for building and improving organizational security programs. This series breaks down every function, category, and subcategory within the CSF, helping professionals, educators, and leaders understand how to apply the framework in real-world environments. Each episode delivers clear, practical explanations that connect framework concepts to daily security operations, governance, and risk management practices. Whether you’re new to cybersecurity or refining an established program, Framework gives you the tools and understanding to align your organization with one of the most trusted security models in the world. Listeners will gain insight into how the CSF’s five core functions—Identify, Protect, Detect, Respond, and Recover—work together to strengthen resilience and reduce cyber risk. The series also explores how organizations can tailor the CSF to their size, sector, and maturity level, integrate it with other standards, and measure progress through profiles and implementation tiers. With practical examples and step-by-step explanations, Framework helps you turn the structure of the CSF into a living, operational roadmap for security success. Developed by **BareMetalCyber.com**, Framework is designed to make cybersecurity standards understandable, actionable, and relevant. Tune in on your favorite platform and build the clarity, confidence, and competence to apply the NIST Cybersecurity Framework in your organization.
Episódios 114
Welcome to Framework: The NIST CSF
Dive into a fast, no-fluff overview of what this podcast delivers, who it’s for, and how each episode helps you level up with practical, real-world takeaways. In this trailer, you’ll hear the show’s promise …
Notas do episódio
Dive into a fast, no-fluff overview of what this podcast delivers, who it’s for, and how each episode helps you level up with practical, real-world takeaways. In this trailer, you’ll hear the show’s promise, the format you can expect, and a sneak peek at the kinds of stories, tips, and expert insights coming your way. Hit follow to get new episodes as they drop and start listening smarter from day one.
RC.CO-04 - Sharing Public Recovery Updates
RC.CO-04 involves sharing public updates on incident recovery using approved channels and messaging, such as breach notifications or preventative steps, to inform affected parties or the broader community. This …
Notas do episódio
RC.CO-04 involves sharing public updates on incident recovery using approved channels and messaging, such as breach notifications or preventative steps, to inform affected parties or the broader community. This ensures transparency about recovery efforts and future safeguards, maintaining public trust. It addresses external expectations post-incident.
This subcategory aligns with legal and risk requirements, ensuring communications are consistent and controlled to avoid misinformation. It supports reputation management by explaining recovery actions clearly and responsibly. RC.CO-04 bridges organizational recovery with public accountability.
RC.CO-03 - Communicating Recovery Progress
RC.CO-03 ensures recovery activities and progress are shared with designated stakeholders—like leadership and suppliers—consistent with response plans and agreements. This includes regular updates on …
Notas do episódio
RC.CO-03 ensures recovery activities and progress are shared with designated stakeholders—like leadership and suppliers—consistent with response plans and agreements. This includes regular updates on restoration status, adhering to contractual protocols for information sharing. It keeps all parties informed and aligned during recovery.
This subcategory aligns communication with risk and operational needs, fostering trust and coordination with critical partners. It supports a unified recovery effort by ensuring transparency on progress and challenges. RC.CO-03 sustains stakeholder engagement through the restoration phase.
RC.RP-06 - Declaring Recovery Completion
RC.RP-06 declares the end of recovery once predefined criteria are met, finalizing the process with a comprehensive after-action report detailing the incident, actions, and lessons learned. This formal closure …
Notas do episódio
RC.RP-06 declares the end of recovery once predefined criteria are met, finalizing the process with a comprehensive after-action report detailing the incident, actions, and lessons learned. This formal closure ensures all steps are documented for review and improvement. It marks the return to full normalcy.
This subcategory aligns with risk management by tying closure to measurable outcomes, ensuring accountability and transparency in recovery efforts. It supports future resilience by capturing insights for refinement. RC.RP-06 concludes recovery with clarity and foresight.
RC.RP-05 - Confirming System Restoration
RC.RP-05 verifies the integrity of restored assets—checking for lingering threats or root causes—before returning systems to production, confirming normal operations. This involves testing restoration adequacy …
Notas do episódio
RC.RP-05 verifies the integrity of restored assets—checking for lingering threats or root causes—before returning systems to production, confirming normal operations. This involves testing restoration adequacy to ensure functionality and security are fully restored. It finalizes recovery with assurance.
This subcategory aligns with risk goals by ensuring restored systems are secure and operational, preventing recurrence from overlooked issues. It supports confidence in recovery outcomes through rigorous validation. RC.RP-05 completes the restoration process with integrity.
RC.RP-04 - Restoring Critical Functions Post-Incident
RC.RP-04 considers critical mission functions and cybersecurity risks to define post-incident operational norms, using impact records to prioritize restoration order. This involves collaboration with system …
Notas do episódio
RC.RP-04 considers critical mission functions and cybersecurity risks to define post-incident operational norms, using impact records to prioritize restoration order. This involves collaboration with system owners to confirm successful recovery and monitor performance for adequacy. It ensures recovery aligns with strategic goals.
This subcategory aligns restoration with risk and mission priorities, ensuring essential services resume first while maintaining security standards. It establishes a sustainable post-incident state, balancing functionality and protection. RC.RP-04 shapes a resilient operational recovery.
RC.RP-03 - Verifying Backup Integrity
RC.RP-03 ensures backups and restoration assets are checked for integrity—free of compromise or corruption—before use in recovery efforts. This verification prevents reintroducing threats or using unreliable …
Notas do episódio
RC.RP-03 ensures backups and restoration assets are checked for integrity—free of compromise or corruption—before use in recovery efforts. This verification prevents reintroducing threats or using unreliable data, safeguarding the restoration process. It guarantees a clean starting point for recovery.
This subcategory aligns with risk management by prioritizing the reliability of recovery tools, reducing the chance of failed restorations. It supports operational continuity by ensuring only trusted assets are deployed. RC.RP-03 underpins a secure recovery foundation.
RC.RP-02 - Prioritizing Recovery Actions
RC.RP-02 involves selecting, scoping, and prioritizing recovery actions based on incident response plan criteria and available resources, adapting as needs shift. This ensures efforts focus on critical systems …
Notas do episódio
RC.RP-02 involves selecting, scoping, and prioritizing recovery actions based on incident response plan criteria and available resources, adapting as needs shift. This ensures efforts focus on critical systems first, balancing speed with effectiveness in execution. It operationalizes recovery with precision.
This subcategory aligns actions with risk and operational goals, ensuring resources address the most impactful areas efficiently. It supports flexibility by allowing reassessment of plans mid-recovery, optimizing outcomes. RC.RP-02 drives a targeted restoration process.
RC.RP-01 - Launching Incident Recovery Efforts
RC.RP-01 initiates the recovery phase of the incident response plan once triggered, ensuring all responsible parties are aware of their roles and required authorizations. This begins during or after …
Notas do episódio
RC.RP-01 initiates the recovery phase of the incident response plan once triggered, ensuring all responsible parties are aware of their roles and required authorizations. This begins during or after containment, focusing on restoring affected systems and services systematically. It transitions the organization from response to recovery.
This subcategory aligns recovery with risk and operational priorities, ensuring a coordinated effort to regain normalcy with minimal disruption. It sets the stage for restoring availability, leveraging predefined plans for efficiency. RC.RP-01 launches the path to operational restoration.
RS.MI-02 - Eradicating Incident Threats
RS.MI-02 ensures incidents are fully eradicated, removing threats like malware or unauthorized access through automated system features or manual responder actions. This can involve third-party support, such as …
Notas do episódio
RS.MI-02 ensures incidents are fully eradicated, removing threats like malware or unauthorized access through automated system features or manual responder actions. This can involve third-party support, such as MSSPs, to eliminate root causes and residual risks. It restores systems to a secure state.
This subcategory aligns eradication with risk goals, ensuring complete threat removal to prevent recurrence, balancing speed with thoroughness. It supports recovery by clearing the path for safe restoration. RS.MI-02 finalizes the mitigation process with decisive action.
RS.MI-01 - Containing Cybersecurity Incidents
RS.MI-01 focuses on containing incidents to prevent their expansion, using automated tools like antivirus or manual actions by responders to isolate threats. This can involve third-party assistance (e.g., ISPs) …
Notas do episódio
RS.MI-01 focuses on containing incidents to prevent their expansion, using automated tools like antivirus or manual actions by responders to isolate threats. This can involve third-party assistance (e.g., ISPs) or redirecting compromised endpoints to remediation VLANs, limiting damage. It stops incidents from spreading further.
This subcategory aligns containment with risk priorities, ensuring rapid action protects critical assets and minimizes disruption. It supports a proactive stance by leveraging both technology and human intervention as needed. RS.MI-01 is the first line of defense in incident mitigation.
RS.CO-03 - Sharing Information with Stakeholders
RS.CO-03 involves sharing incident information with designated stakeholders—both internal, like leadership, and external, like ISACs—consistent with response plans and agreements. This includes voluntary …
Notas do episódio
RS.CO-03 involves sharing incident information with designated stakeholders—both internal, like leadership, and external, like ISACs—consistent with response plans and agreements. This includes voluntary sharing of anonymized attack data or updates on insider threats with HR, enhancing situational awareness. It ensures relevant parties stay informed.
This subcategory strengthens response by aligning information flow with contractual rules and crisis protocols, such as supplier coordination. It promotes broader cybersecurity collaboration while protecting sensitive data. RS.CO-03 builds a network of informed responders and supporters.
RS.CO-02 - Notifying Stakeholders of Incidents
RS.CO-02 ensures timely notification of internal and external stakeholders—like customers, partners, or regulators—about incidents, following breach procedures or contractual obligations. This includes …
Notas do episódio
RS.CO-02 ensures timely notification of internal and external stakeholders—like customers, partners, or regulators—about incidents, following breach procedures or contractual obligations. This includes notifying law enforcement when criteria and approvals dictate, maintaining transparency and compliance. It keeps affected parties informed and engaged.
This subcategory aligns communication with legal and risk requirements, reducing delays in critical notifications that could impact trust or recovery. It supports coordinated response by ensuring stakeholders know their roles or risks. RS.CO-02 fosters a collaborative incident response ecosystem.
RS.AN-08 - Assessing Incident Magnitude
RS.AN-08 estimates and validates an incident’s magnitude by assessing its scope and impact, searching other targets for indicators of compromise or persistence. This involves manual reviews or automated tools …
Notas do episódio
RS.AN-08 estimates and validates an incident’s magnitude by assessing its scope and impact, searching other targets for indicators of compromise or persistence. This involves manual reviews or automated tools to confirm the extent of damage or spread, refining initial assessments. It quantifies the incident’s true reach.
This subcategory aligns analysis with risk priorities, ensuring resources target the full breadth of an incident, from isolated to systemic effects. It supports effective mitigation by clarifying the scale of response needed. RS.AN-08 ensures a comprehensive grasp of incident consequences.
RS.AN-07 - Preserving Incident Data Integrity
RS.AN-07 focuses on collecting and preserving incident data and metadata—such as source and timestamps—using chain-of-custody procedures to ensure integrity. This comprehensive gathering supports forensic …
Notas do episódio
RS.AN-07 focuses on collecting and preserving incident data and metadata—such as source and timestamps—using chain-of-custody procedures to ensure integrity. This comprehensive gathering supports forensic analysis and compliance, protecting evidence from alteration. It ensures data remains a trustworthy resource for investigation.
This subcategory aligns with risk and legal requirements, safeguarding critical information for root cause analysis and reporting. It enhances response accuracy by maintaining a pristine data set for review. RS.AN-07 underpins robust incident analysis and recovery.
RS.AN-06 - Recording Investigation Actions
RS.AN-06 ensures that all investigative actions during an incident—like system checks or containment steps—are meticulously recorded, with integrity and provenance preserved. This involves immutable logs by …
Notas do episódio
RS.AN-06 ensures that all investigative actions during an incident—like system checks or containment steps—are meticulously recorded, with integrity and provenance preserved. This involves immutable logs by responders and detailed documentation by the incident lead, safeguarding evidence for legal or audit purposes. It maintains a reliable investigation trail.
This subcategory supports accountability and forensics by ensuring records are tamper-proof and traceable, aligning with risk management needs. It enables accurate post-incident reviews and lessons learned, enhancing future responses. RS.AN-06 upholds the credibility of incident investigations.
RS.AN-03 - Investigating Incident Causes
RS.AN-03 conducts detailed analysis to reconstruct incident events, identify involved assets, and pinpoint root causes, such as exploited vulnerabilities or threat actors. This includes examining deception …
Notas do episódio
RS.AN-03 conducts detailed analysis to reconstruct incident events, identify involved assets, and pinpoint root causes, such as exploited vulnerabilities or threat actors. This includes examining deception technologies for attacker behavior insights, aiming to understand both immediate triggers and systemic issues. It provides the foundation for effective response and prevention.
This subcategory enhances response by delivering actionable findings, aligning analysis with risk priorities to address critical weaknesses. It supports forensics and recovery by uncovering underlying causes, reducing recurrence risks. RS.AN-03 drives a thorough understanding of incident dynamics.
RS.MA-05 - Initiating Incident Recovery
RS.MA-05 applies predefined criteria to determine when to shift from response to recovery, based on incident characteristics and operational considerations. This decision balances containment success with …
Notas do episódio
RS.MA-05 applies predefined criteria to determine when to shift from response to recovery, based on incident characteristics and operational considerations. This decision balances containment success with potential disruptions from recovery actions, ensuring a smooth transition. It marks the pivot to restoring normalcy.
This subcategory aligns recovery initiation with risk and operational priorities, preventing premature or delayed action that could worsen impacts. It ensures a deliberate, criteria-driven approach to recovery planning. RS.MA-05 facilitates a seamless move from mitigation to restoration.
RS.MA-04 - Escalating Incidents When Needed
RS.MA-04 ensures incidents are escalated or elevated to higher levels of authority or expertise when their complexity or impact exceeds initial handling capabilities. This involves tracking incident status and …
Notas do episódio
RS.MA-04 ensures incidents are escalated or elevated to higher levels of authority or expertise when their complexity or impact exceeds initial handling capabilities. This involves tracking incident status and coordinating with designated stakeholders, both internal and external, for additional support. It maintains control over evolving incidents.
This subcategory aligns escalation with risk thresholds, ensuring timely involvement of senior leadership or specialists as needed. It enhances response flexibility by validating progress and adjusting resources dynamically. RS.MA-04 keeps incident management responsive to changing demands.
RS.MA-03 - Categorizing and Prioritizing Incidents
RS.MA-03 categorizes incidents—such as ransomware or data breaches—and prioritizes them based on scope, impact, and urgency, balancing rapid recovery with investigation needs. This detailed review assigns …
Notas do episódio
RS.MA-03 categorizes incidents—such as ransomware or data breaches—and prioritizes them based on scope, impact, and urgency, balancing rapid recovery with investigation needs. This detailed review assigns incidents to specific response strategies, ensuring appropriate resource allocation. It organizes chaos into actionable steps.
This subcategory aligns response efforts with organizational priorities, focusing on high-impact events while preserving evidence where needed. It supports strategic decision-making by classifying incidents systematically. RS.MA-03 optimizes the response process for efficiency and effectiveness.
RS.MA-02 - Triaging and Validating Incident Reports
RS.MA-02 involves triaging and validating incident reports to confirm their cybersecurity relevance and need for response, applying severity criteria to prioritize action. This preliminary review filters out …
Notas do episódio
RS.MA-02 involves triaging and validating incident reports to confirm their cybersecurity relevance and need for response, applying severity criteria to prioritize action. This preliminary review filters out non-issues, ensuring resources focus on genuine threats like breaches or malware. It streamlines the initial handling of reported events.
This subcategory enhances efficiency by quickly assessing incident legitimacy, aligning efforts with risk priorities. It provides a clear entry point for response, reducing delays in addressing critical incidents. RS.MA-02 ensures that only validated threats proceed to deeper management.
RS.MA-01 - Executing the Incident Response Plan
RS.MA-01 initiates the execution of the incident response plan in coordination with third parties—like outsourcers or suppliers—once an incident is confirmed. This includes designating an incident lead and …
Notas do episódio
RS.MA-01 initiates the execution of the incident response plan in coordination with third parties—like outsourcers or suppliers—once an incident is confirmed. This includes designating an incident lead and activating additional plans (e.g., business continuity) as needed to support response efforts. It ensures a structured, collaborative approach to managing incidents.
This subcategory aligns response actions with organizational and external capabilities, leveraging automation or external assistance for efficiency. It minimizes disruption by integrating third-party roles into the response framework, enhancing effectiveness. RS.MA-01 sets the stage for a unified incident handling process.
DE.AE-08 - Declaring Incidents Based on Criteria
DE.AE-08 involves declaring incidents when adverse events meet predefined criteria, such as severity or scope, ensuring a formal response is triggered. This process accounts for known false positives to avoid …
Notas do episódio
DE.AE-08 involves declaring incidents when adverse events meet predefined criteria, such as severity or scope, ensuring a formal response is triggered. This process accounts for known false positives to avoid unnecessary escalation, applying criteria to event characteristics systematically. It marks the transition from detection to response.
This subcategory ensures consistency in incident identification, aligning declarations with risk management priorities and operational impact. It provides a clear threshold for action, enabling timely mitigation efforts. DE.AE-08 formalizes the shift to incident management with precision.
DE.AE-07 - Enhancing Analysis with Threat Intelligence
DE.AE-07 integrates cyber threat intelligence and contextual data—like asset inventories or vulnerability disclosures—into adverse event analysis to enhance accuracy and relevance. This involves securely …
Notas do episódio
DE.AE-07 integrates cyber threat intelligence and contextual data—like asset inventories or vulnerability disclosures—into adverse event analysis to enhance accuracy and relevance. This involves securely feeding intelligence to detection technologies and personnel, enabling rapid analysis of supplier or third-party advisories. It enriches understanding of event significance.
This subcategory strengthens detection by providing a broader context, aligning analysis with the organization’s specific risk profile and technology stack. It ensures that external insights inform internal responses, reducing false positives and missed threats. DE.AE-07 connects global intelligence to local action.
DE.AE-06 - Sharing Adverse Event Information
DE.AE-06 ensures that information about adverse events is promptly shared with authorized staff—such as SOC teams and incident responders—and integrated into response tools. This includes generating alerts …
Notas do episódio
DE.AE-06 ensures that information about adverse events is promptly shared with authorized staff—such as SOC teams and incident responders—and integrated into response tools. This includes generating alerts, assigning tickets in ticketing systems, and providing access to analysis findings at all times. It enables swift, coordinated action against detected threats.
This subcategory enhances response efficiency by aligning information delivery with operational needs, ensuring the right people and systems are informed. It supports both automated and manual workflows, reducing delays in addressing events. DE.AE-06 bridges detection and response with timely communication.
DE.AE-04 - Estimating the Impact of Adverse Events
DE.AE-04 estimates the impact and scope of adverse events to gauge their potential harm, using tools like SIEMs or manual analysis to assess affected assets and severity. This process refines initial estimates …
Notas do episódio
DE.AE-04 estimates the impact and scope of adverse events to gauge their potential harm, using tools like SIEMs or manual analysis to assess affected assets and severity. This process refines initial estimates through review, ensuring a clear understanding of consequences like data loss or downtime. It informs prioritization of response efforts.
This subcategory aligns analysis with risk management by quantifying event effects, supporting resource allocation and escalation decisions. It ensures that the organization grasps the full extent of a threat, from isolated incidents to systemic risks. DE.AE-04 provides critical context for effective incident handling.
DE.AE-03 - Correlating Data from Multiple Sources
DE.AE-03 correlates information from diverse sources—like logs, sensors, and threat intelligence—to build a unified picture of potential adverse events. This involves consolidating log data into centralized …
Notas do episódio
DE.AE-03 correlates information from diverse sources—like logs, sensors, and threat intelligence—to build a unified picture of potential adverse events. This involves consolidating log data into centralized servers and using event correlation tools (e.g., SIEM) to identify patterns or connections. It enhances detection by linking disparate clues into coherent threats.
This subcategory strengthens analysis by integrating external intelligence with internal data, improving the accuracy of event characterization. It supports a holistic view of the threat landscape, aligning correlation with risk priorities. DE.AE-03 amplifies the power of individual monitoring efforts.
DE.AE-02 - Analyzing Adverse Events for Insights
DE.AE-02 focuses on analyzing potentially adverse events to understand their nature, using tools like SIEM systems to examine log events for malicious or suspicious activity. This includes leveraging cyber …
Notas do episódio
DE.AE-02 focuses on analyzing potentially adverse events to understand their nature, using tools like SIEM systems to examine log events for malicious or suspicious activity. This includes leveraging cyber threat intelligence to characterize threat actors, tactics, and indicators of compromise, supplemented by manual reviews where automation falls short. It turns raw detections into actionable insights.
This subcategory improves detection accuracy by providing detailed context about event origins and methods, supporting informed response decisions. It ensures thorough analysis across all technologies, aligning efforts with risk priorities. DE.AE-02 bridges monitoring and incident characterization for effective threat management.
DE.CM-09 - Detecting Threats Across Technology Stacks
DE.CM-09 involves monitoring hardware, software, runtime environments, and associated data to detect adverse events like malware, phishing, or tampering. This includes tracking authentication attempts …
Notas do episódio
DE.CM-09 involves monitoring hardware, software, runtime environments, and associated data to detect adverse events like malware, phishing, or tampering. This includes tracking authentication attempts, configuration changes, and endpoint health to identify risks such as unauthorized software or credential attacks. It ensures a deep, system-level view of potential threats.
This subcategory enhances security by using endpoint technologies to redirect compromised devices for remediation, aligning monitoring with risk priorities. It provides comprehensive coverage of common attack vectors like email or file sharing, enabling rapid response. DE.CM-09 underpins a robust detection framework across the technology stack.
DE.CM-06 - Monitoring External Service Providers
DE.CM-06 requires monitoring the activities and services of external providers—like cloud platforms or ISPs—to detect adverse events that could impact the organization. This includes tracking remote …
Notas do episódio
DE.CM-06 requires monitoring the activities and services of external providers—like cloud platforms or ISPs—to detect adverse events that could impact the organization. This includes tracking remote administration or onsite maintenance by third parties for deviations from expected behavior. It ensures external dependencies don’t become blind spots.
This subcategory mitigates risks from outsourced services by maintaining oversight, aligning monitoring with contractual security expectations. It supports a comprehensive security posture by extending vigilance beyond organizational boundaries. DE.CM-06 safeguards against threats originating in the supply chain.
Aqui estão os 60 episódios mais recentes de 114. Os mais antigos estão no feed do podcast.
Recomendado por Framework: The NIST Cybersecurity Framework (CSF)






Podcasts parecidos
Mais podcasts de Educação
Este podcast é seu?
Confirme com uma entrada no seu feed: você recebe um código aqui, adiciona como podcast:txt no canal do seu feed e nós verificamos. Depois disso, seu podcast aparece como “verificado” no SoundNode.